

- ABOUT US
- INSPECTION VALIDITY CHECK
- VEHICLE INSPECTION STATIONS (STK)
- FOR THE PUBLIC
- REGULATIONS
- CONTACT
 13.02.2026
On 9 February 2026, between 10:01 and 10:17, we recorded a growing number of requests to the “Closed inspections” form. The specific feature of these requests was that the user repeatedly requested a very long time range for the selection of data on closed inspections, which caused extreme load on the DB server.
At the same time, during this period, we recorded a very high number of login requests to CIS TK (from one inspection station), with a maximum of 418 requests in a single minute. As in the case of the incident of 30 September 2025, this activity came from the account of technician Ing. D. T., who is a technician of the authorised entity XXX (inspection station No. XXX).
These requests caused a high load on the DB server and an increase in the request queue. As a result, between 10:01 and 10:17 the response time of CIS TK gradually slowed down and, in some cases, users’ requests were rejected.
The incident can be classified as a locally induced DoS (Denial of Service) incident, while the intent behind the requests to the “Closed inspections” form cannot be assessed unequivocally.
In the case of repeated login requests, this conduct can be classified as deliberate and intentional, using external software tools to automate communication and perform data mining while using valid access permissions. Since CIS TK has technical measures implemented against data mining using such procedures (and therefore no data from CIS TK are disclosed), the likely objective of the attacker is to disrupt the operation of CIS TK and damage the operator and other users of CIS TK.
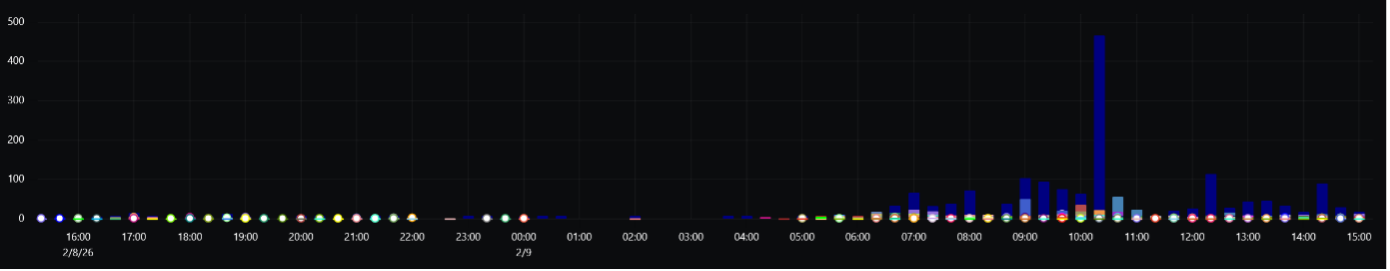
Total number of requests to Closed inspections, with the inspection station showing dominant activity highlighted in blue for 8 Feb 2026 15:20 – 9 Feb 2026 15:00
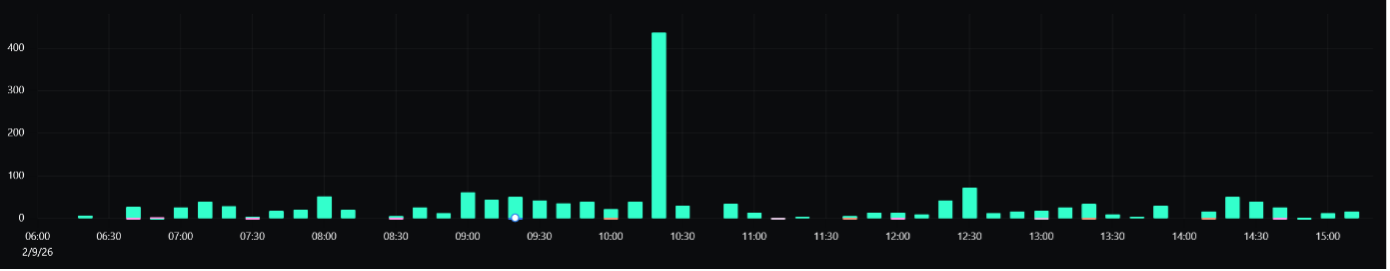
Number of login requests to CIS TK for 9 Feb 2026 6:15–15:15
Impact
CIS TK did not experience a complete outage. A slowdown in system response lasting 16 minutes (10:01–10:17) was recorded, and in some cases requests from some authorised users were rejected.
Proposed measures
With regard to the high load generated by the “Closed inspections” form, we have deployed a solution optimising the number of queries to the DB server. At the same time, we will adjust the rules for selecting closed inspections and limit the maximum scope of the selected data.
We will continue to consistently monitor infrastructure operating parameters, perform forensic analysis of causes, detect sources of possible anomalies and identify responsible actors and their procedures. Based on the established facts, we will take the appropriate steps to hold accountable the persons carrying out activities that are contrary to the law.
At the same time, we call on users to use CIS TK responsibly, solely for the purpose for which it is intended, and through regularly updated versions of supported browsers (Google Chrome, Mozilla Firefox, Microsoft Edge, Apple Safari). We also remind users of their responsibility for activities carried out towards CIS TK in their name and of the obligation to protect the credentials of their assigned user account, not to disclose them or share them with anyone, and, if they are compromised, to change the CIS TK login password without delay. Likewise, we call on users to prevent other persons from accessing CIS TK when they are absent from the workplace.